
iso360 has announced the appointment of co-founder Sharon Buck as Chief Executive Officer, marking an important milestone as we enter our next phase of growth.
While Sharon and fellow co-founder Gray Millen will continue to shape the strategic direction of the business together, the appointment formalises a leadership structure that has developed naturally as the company has expanded.
“For the team, it’s important to have one clear operational leader,” Sharon explains. “Gray and I have always been completely aligned, but as the business grows, people need clarity. We’ll still make the big decisions together behind the scenes, but day-to-day leadership now sits with me.”
The move comes after a significant period of growth for iso360, which has expanded from a two-person consultancy in 2018 to a specialist team of seven, with plans to more than double in size over the next two to three years.
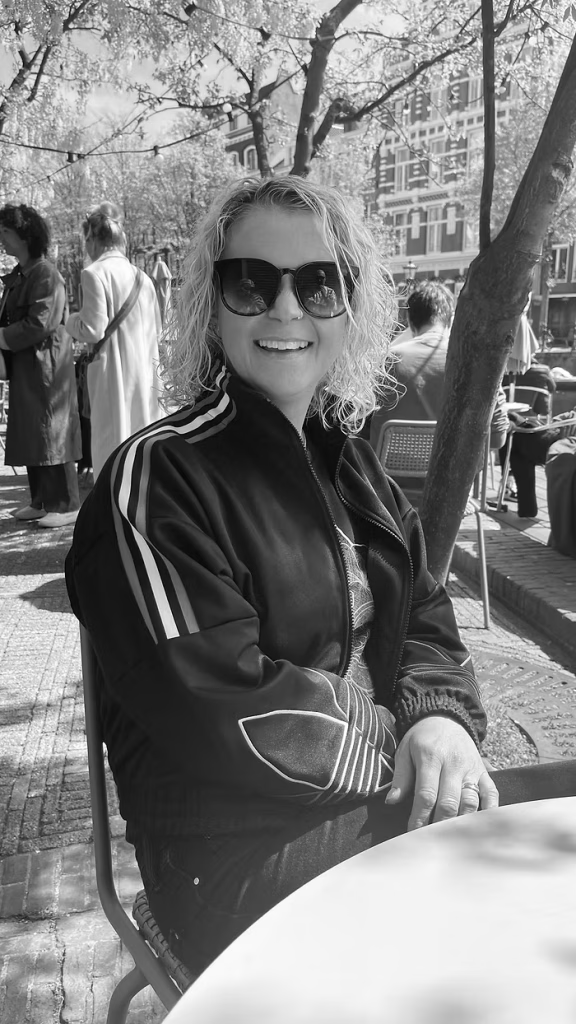
From graduate to CEO
Sharon’s career in risk, resilience and compliance began after graduating with a business degree and moving to Bristol. There, she joined the Bank of Ireland as a Business Continuity Coordinator.
Working alongside an experienced mentor, Sharon found herself drawn to helping organisations prepare for disruption and manage risk.
Senior roles at Citigroup and Liberata followed, before she became Head of Risk and Compliance at Trustmarque, overseeing information security, governance and compliance across government, defence and managed service contracts.
The partnership behind ISO360
Although both had successful corporate careers, Sharon had always imagined running her own business and conversations with Gray revealed shared personal interests and professional goals.
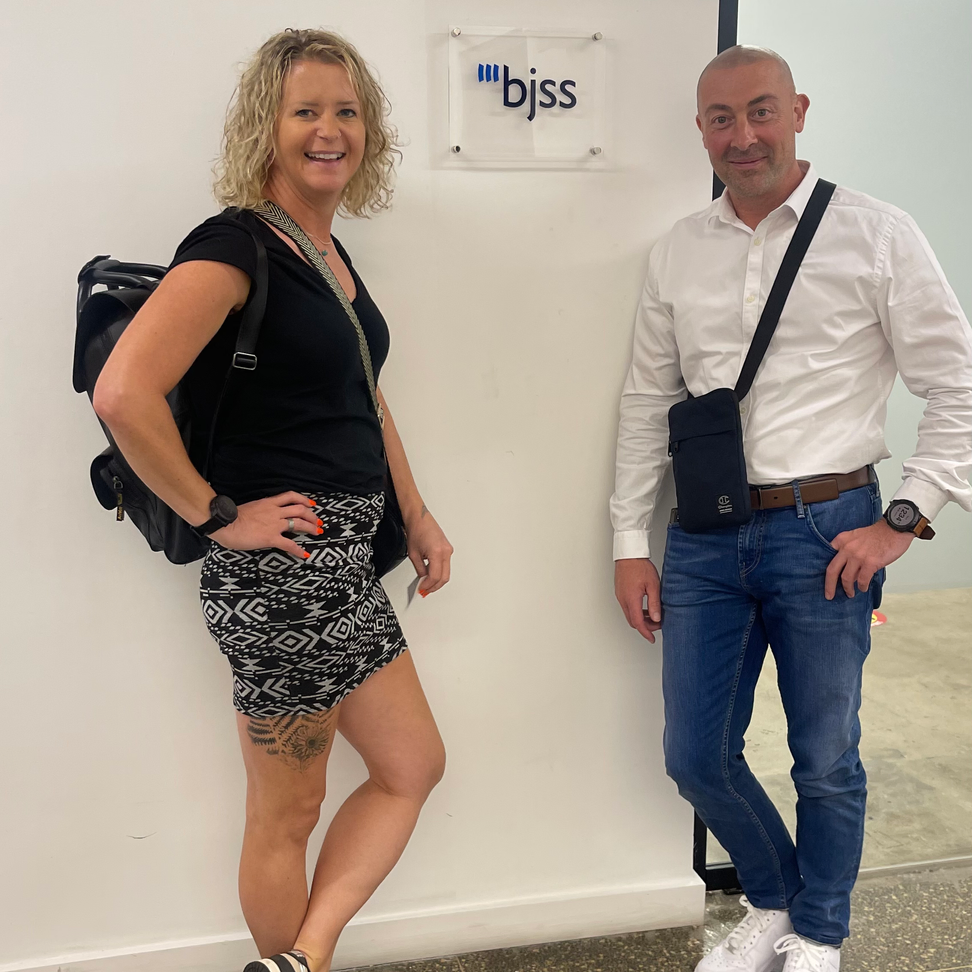
She says: “Gray and I hit it off and worked well together. I’d always imagined myself working as a lone consultant, but we quickly realised two minds were better than one.”
The pair officially launched iso360 in 2018, combining Gray’s technical information security expertise with Sharon’s operational leadership and compliance background, and their contrasting personalities have become one of the company’s biggest strengths.
Sharon adds: “We’ve never competed with each other which is quite unusual. Gray is full of ideas and vision, while I’m much steadier operationally. We complement each other.”
A natural evolution
While Sharon’s CEO announcement is new, the leadership transition has evolved naturally behind the scenes.
Over the past eighteen months, Sharon has taken responsibility for the day-to-day running of iso360.
Sharon says: “It happened quite naturally, and we realised it was actually the right structure for the business.”
Gray adds: “Sharon has been living and breathing iso360 since day one, but especially over the last year. This appointment recognises the role she’s already been doing exceptionally well.”
Looking ahead
The appointment comes as iso360 prepares for its next phase of evolution and expansion.
The leadership team has developed a five-year growth plan that includes doubling headcount while continuing to specialise in supporting technology businesses, software companies, and medical device organisations with information security, governance and compliance.
Recent additions to the team reflect that strategy, with specialists joining in AI governance, GDPR, auditing, operations and medical device compliance.
Rather than becoming a large corporate, iso360 intends to maintain its position as a boutique consultancy supporting growing businesses that need practical, streamlined compliance support without unnecessary complexity.
“The company is always evolving but the vision hasn’t changed,” says Sharon. “We want to build a brilliant team, work with clients we love and prove that compliance doesn’t have to be complex.”
With a clear leadership structure now in place, iso360 is well positioned for the next chapter of its journey.
Get in touch with Sharon to enquire about governance, risk, compliance, or cyber security management support.