
At iso360, our team is handpicked carefully. And not just for their expertise and qualifications, but also for their personalities, genuine commitment to our clients, and how they support our company culture and team dynamic. In this instalment of our ‘Meet the Team’ series, we’re sitting down with Senior Auditor Frances Heap.
Fran embodies the honest, partnership-driven approach we take to your compliance and data security needs. Learn more about Fran’s journey and why she loves helping clients navigate the world of compliance.
What’s your role at ISO360, and what does it involve day to day?
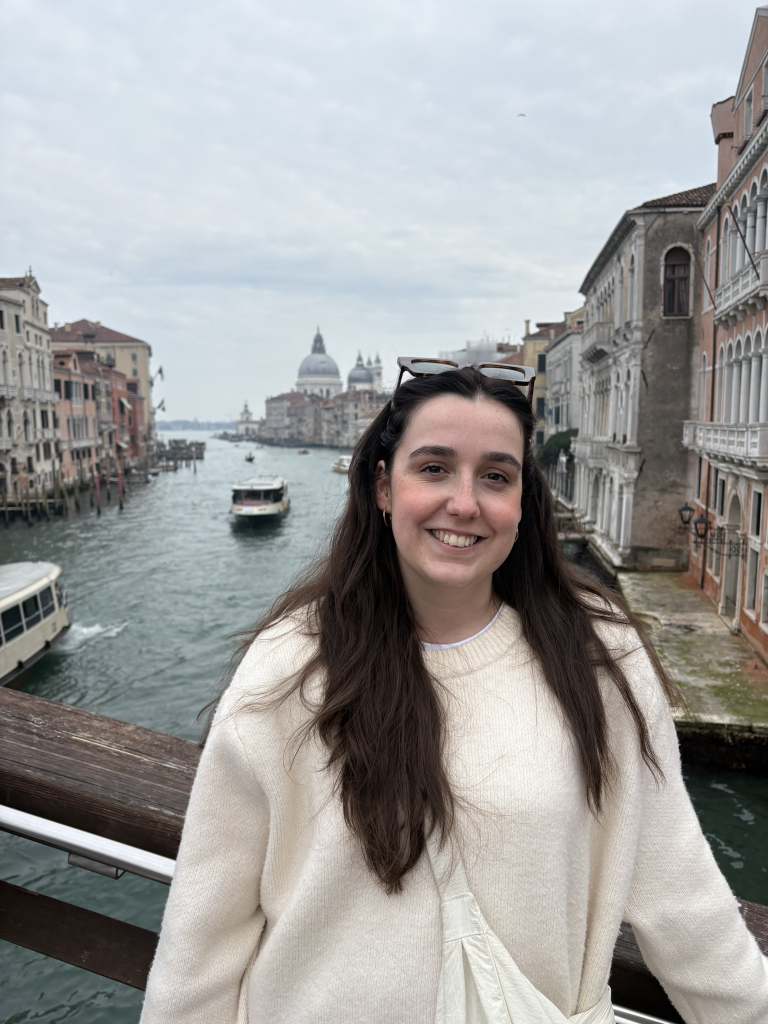
I’m a Senior Auditor.
My day-to-day involves checking in with customers to see how they are and what they’ve been up to, as well as identifying any changes in their business.
I audit them depending on the specific standard required.
Quite a few clients have integrated management systems now, which has changed the way we audit by looking at a wider scope than just one standard.
I also run point on some accounts as the first point of contact and help out where needed.
We maintain a clear distinction where you can’t have the same consultant and internal auditor, so there are often two of us on one account.
What did you do before joining ISO360?
I have a background in politics. I studied at Lincoln and then Sheffield for a Masters in Policy Governance and Public Policy. I became interested in governance processes and how things work, writing my dissertation on improving the private members’ bill process.
How did you first get into cybersecurity, compliance, or your particular area of work?
My path started at BJSS when I got involved with developing a supplier management process. I found I had a taste for understanding what a company needs and what needs to be considered. This led me to move into information security, leveraging my background in governance and policy, and I eventually earned my certification as a lead auditor.
What brought you to iso360?
I knew Gray for three years as he was my consultant at BJSS. We got on well and I liked the business because it was “no bullshit.” When the opportunity came up, I started in April 2025 and have been here just over a year. It’s changed so much since then. More customers, more staff, and a lot of scaling up.
What do you enjoy most about your role?
I really enjoy talking to people. Audits can be dry and it’s not everyone’s favourite thing in the world to sit in front of an auditor being asked loads of questions, so I like breaking the perception that auditors are boring people in suits with a clipboard telling you off.
Being from Leeds and working with many Leeds-based customers, I enjoy helping them and getting to know them. We like to integrate into teams and become an extension of them.
What are your particular strengths or areas of expertise?
Within ISO 27001, I like the supplier side of things, which is what kicked off my career in this world.
I also like the legal and political sides of the work. I got my ISO 42001 lead auditor certification last year and I find the societal side of AI and how it integrates with other changes really interesting.
What do you think you bring to the team that’s uniquely you?
I am very honest in the way I interact. I also really enjoy working in a team and it’s been great to see the team grow over the last year. I value supporting each other and learning different things from one another.
What’s a project, achievement, or career moment you’re especially proud of?
I’m proud of developing the contracts we already had and working hard to support clients through their internal audits. A recent client didn’t get a single finding in their external audit in July. That was a great moment.
What do clients tend to appreciate most about working with you?
Clients appreciate the honest and direct approach. I try to make them feel comfortable and work as an extension of their team.
How would you describe the culture at iso360?
The culture is very open and honest. It’s not very “corporate” in the traditional sense; you can truly be yourself without having to censor your personality. Because the team is handpicked, there is a high level of trust and everyone is very to-the-point.
What makes iso360 different from other companies you’ve worked for?
You don’t have to wear a “corporate mask.” Gray and Sharon hire based on personality as much as experience, making sure the team gets on well. It feels like a collection of handpicked people you can trust.
How have you been supported to learn, develop, or progress since joining?
I completed the ISO 42001 lead auditor course last year. I’ve also been given the opportunity to mentor new team members like Siju. It’s been a real team effort and that’s been nice, being able to pass my knowledge on.
I’ve also got a CISA course coming up soon. Sharon and Gray are always very supportive of anything we want to do – and they also listen if it’s something we don’t want to do. It’s very much a discussion.
Who are you outside work?
Outside of work, I play netball, see friends, and go to the gym. I am a big reader, I also love travelling and making plans for the weekend.
What are you looking forward to next, professionally or personally?
I’m looking forward to continuing our growth and moving more into consultancy as Siju takes over some audits. We’re going to be at Leeds Digital Festival again – I’m organising this with Abi and I’m really excited about it, I’m looking forward to building on existing customer relationships and getting our name out there more.
Want to feel confident and prepared for your next audit? Get in touch to find out how Fran and the iso360 team can help.